Why Linux Admins Fear (and Love) chmod 777—The Powerful File Permissions Command Explained

The `chmod 777` command is a double-edged sword in Unix-based systems. On one hand, it grants full read, write, and execute permissions to everyone—owner, group, and others—making file access effortless. On the other, it dismantles security boundaries, exposing sensitive data to unauthorized users. System administrators often debate its necessity, balancing convenience against vulnerability. Even seasoned developers occasionally reach for it in desperation, only to later regret the oversight.
Yet, understanding `chmod 777` isn’t just about memorizing the syntax. It’s about grasping the philosophy behind Unix permissions—how ownership, groups, and world access interact to define system integrity. Misuse can lead to exploits, while proper application can streamline workflows. The command’s simplicity belies its complexity: a three-digit octal number that encodes granular control over who can interact with a file or directory.
For developers deploying scripts, web servers configuring upload directories, or sysadmins troubleshooting permission errors, `chmod 777` is a tool that demands respect. Its reputation as a "quick fix" often masks deeper issues in file ownership or system architecture. The key lies in knowing when to wield it—and when to seek alternatives.
The Complete Overview of chmod 777
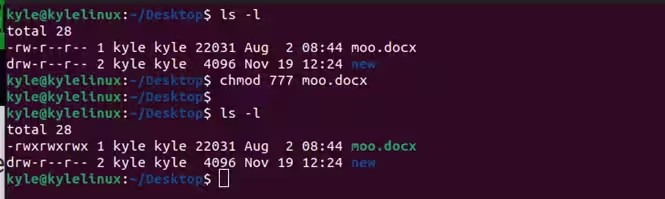
`chmod 777` is shorthand for "change mode" in Unix-like operating systems, where permissions are assigned using octal notation. The three digits represent permissions for the file owner (user), the group, and others (world), respectively. Each digit combines three operations: read (4), write (2), and execute (1). Summing these values—4+2+1—yields 7 for full access. Thus, `777` means every entity (owner, group, others) has read, write, and execute privileges.
While the command is straightforward, its implications are profound. In a multi-user environment, granting world-writable permissions (`777`) can turn a secure system into a playground for attackers. Directories with `777` settings, for instance, allow strangers to upload malicious files, execute arbitrary scripts, or even delete critical data. Yet, in isolated development environments or tightly controlled servers, `777` might be a temporary necessity—if used judiciously.
Historical Background and Evolution
The concept of file permissions traces back to the early days of Unix, where resource sharing required strict access control. The `chmod` command emerged as a utility to manage these permissions efficiently. Originally, permissions were set via symbolic notation (e.g., `u=rwx,g=rx,o=rx`), but octal notation simplified the process, allowing administrators to assign permissions in a single step. The `777` combination became infamous as a "nuclear option" for permissions, often applied in haste during system migrations or emergency fixes.
Table of Contents
- The Complete Overview of chmod 777
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Is chmod 777 ever safe to use?
- Q: Why do some applications (e.g., WordPress) require 777 permissions?
- Q: How can I audit my system for chmod 777 directories?
- Q: What’s the difference between chmod 777 and chmod a+rwx ?
- Q: Can I restrict chmod 777 usage in my organization?
- Q: What’s the most secure alternative to chmod 777 for shared directories?
As Unix evolved into Linux and other modern OSes, the need for granularity grew. Alternatives like Access Control Lists (ACLs) and SetUID/SetGID bits expanded permission management beyond the rigid `chmod` model. However, `chmod 777` persists in legacy scripts, shared hosting environments, and quick-and-dirty solutions—despite its security flaws. Its longevity reflects a broader tension in system administration: balancing flexibility with security.
Core Mechanisms: How It Works
Under the hood, `chmod 777` modifies the file’s permission bits in the inode, a data structure storing metadata about the file. The octal values (777) translate to binary flags: `111` for owner, `111` for group, and `111` for others. Each `1` corresponds to a permission (read/write/execute). When executed, the command bypasses the default umask (user file-creation mask), which typically restricts new files to `644` (read/write for owner, read-only for others).
Directories behave differently: execute permission (`x`) is required to `cd` into them, while write permission (`w`) allows file creation/deletion. Thus, a `777` directory grants full control to everyone—potentially catastrophic. The command’s simplicity masks its destructive potential: a single misplaced `chmod 777` on `/tmp` or a web root directory can compromise an entire system. Understanding these mechanics is critical to mitigating risks.
Key Benefits and Crucial Impact
Despite its dangers, `chmod 777` offers undeniable advantages in specific scenarios. For developers testing scripts in isolated environments, it eliminates permission-related errors, allowing seamless execution. System administrators managing shared directories (e.g., for group collaboration) might temporarily use `777` to ensure all members can modify files. Even in production, certain applications—like content management systems (CMS)—require world-writable directories for uploads, though `777` is rarely the optimal solution.
The command’s impact extends beyond functionality. It reflects broader trends in system administration: the trade-off between security and usability. While `777` can accelerate workflows, its overuse signals deeper issues—poorly designed permission models, lack of ACLs, or misconfigured ownership. Recognizing these patterns is essential for long-term system health.
"Permission settings are the first line of defense in Unix systems. `chmod 777` is like leaving your front door unlocked—convenient in an emergency, but a security nightmare in the long run."
— Michael Widenius, MySQL Co-Founder
Major Advantages
- Rapid Problem Resolution: Resolves permission errors instantly, especially in development or testing phases where speed outweighs security concerns.
- Shared Environment Access: Enables collaborative editing in group directories where strict ownership isn’t feasible (e.g., team project folders).
- Legacy System Compatibility: Older applications or scripts may explicitly require `777` permissions to function, forcing admins to accommodate them.
- Temporary Fixes: Useful in emergencies (e.g., recovering a locked file) before applying stricter permissions.
- Simplicity: Avoids complex ACLs or group management when broad access is genuinely needed.
Comparative Analysis
While `chmod 777` is a blunt instrument, alternatives offer finer control. Below is a comparison of permission strategies:
| Method | Use Case |
|---|---|
chmod 777 |
Quick fixes, shared dev environments, legacy apps. High risk. |
chmod 755 (Owner: rwx, Group/Others: rx) |
Balanced access for directories (e.g., web roots). Moderate risk. |
| ACLs (Access Control Lists) | Granular permissions beyond user/group/others. Low risk. |
| SetGID (sgid) Bit | Inherits group permissions for new files in a directory. Low risk. |
| Sticky Bit (1777) | Restricts deletion/modification of files in shared directories (e.g., `/tmp`). Low risk. |
The table highlights that `chmod 777` is rarely the best long-term solution. Alternatives like ACLs or SetGID provide security without sacrificing functionality. However, in constrained environments (e.g., shared hosting), `777` may remain the only viable option.
Future Trends and Innovations
The future of file permissions lies in automation and policy-driven management. Tools like selinux and apparmor enforce mandatory access controls (MAC), reducing reliance on manual `chmod` adjustments. Containerization (Docker, Kubernetes) further isolates permissions, limiting the damage of overly permissive settings. Meanwhile, AI-driven security audits could flag `777` usage in real-time, suggesting safer alternatives.
Developers are also adopting "permissionless" architectures, where applications handle access control internally (e.g., database-level permissions). This shift reduces the need for broad file-system permissions like `777`, aligning with zero-trust security models. As systems grow more complex, the days of `chmod 777` as a default may fade—but understanding its mechanics remains vital for legacy systems and edge cases.

Conclusion
`chmod 777` embodies the tension between convenience and security in Unix systems. While it solves immediate problems, its overuse undermines system integrity. The command’s persistence in the wild reflects a cultural inertia: the habit of reaching for the nuclear option when finer tools exist. Moving forward, administrators should treat `777` as a last resort, favoring ACLs, SetGID, or application-level permissions instead.
Ultimately, mastering `chmod 777` isn’t about memorizing the command—it’s about understanding the principles of least privilege and secure design. The next time you’re tempted to type `chmod 777`, pause and ask: Is this the safest path, or am I papering over a deeper flaw? The answer often reveals more about system architecture than the command itself.
Comprehensive FAQs
Q: Is chmod 777 ever safe to use?
A: Only in highly controlled environments, such as isolated development machines or directories with no sensitive data. Even then, it should be temporary and replaced with stricter permissions (e.g., `755` for directories, `644` for files) as soon as possible. Avoid using it on production servers, shared directories, or any path containing executable scripts.
Q: Why do some applications (e.g., WordPress) require 777 permissions?
A: Many applications, especially older ones, are designed with broad permissions in mind due to legacy hosting constraints. WordPress, for example, defaults to `755` for directories and `644` for files, but some shared hosting providers enforce `777` on uploads directories (`/wp-content/uploads`). This is a workaround for misconfigured servers—ideally, the application should handle permissions dynamically.
Q: How can I audit my system for chmod 777 directories?
A: Use the following command to find world-writable directories:
find / -type d -perm -o=w 2>/dev/null
For files:
find / -type f -perm -o=w 2>/dev/null
This will list all directories/files writable by "others," including those with `777` permissions. Review these paths critically—many may be unnecessary risks.
Q: What’s the difference between chmod 777 and chmod a+rwx?
A: Both commands achieve the same result: granting read, write, and execute permissions to owner, group, and others. However, `777` uses octal notation (faster to type), while `a+rwx` uses symbolic notation (more verbose but potentially clearer for beginners). The choice is stylistic, though `777` is more common in scripts and automation.
Q: Can I restrict chmod 777 usage in my organization?
A: Yes. Implement policies requiring code reviews for `chmod` commands or use tools like auditd to log permission changes. Enforce stricter defaults (e.g., `umask 027`) to limit world-writable files by default. Combine this with regular security audits to catch over-permissive settings early.
Q: What’s the most secure alternative to chmod 777 for shared directories?
A: Use a combination of:
chmod 775(owner/group: rwx, others: rx) for directories.- ACLs to grant specific users write access without world permissions.
- The sticky bit (
chmod 1777) to prevent others from deleting/modifying files in shared directories (e.g., `/tmp`).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Seuclienteoculto.