Why HTTPS Dominates: The Critical http vs https Showdown for Security and Trust

The first time a browser displayed a red "Not Secure" warning in the address bar, it marked a turning point. Users who had spent years ignoring the subtle "http://" prefix suddenly noticed—because search engines and browsers had made it impossible to ignore. The shift from HTTP to HTTPS wasn’t just an upgrade; it was a security mandate, a trust signal, and an SEO necessity all rolled into one. Yet for many website owners, the distinction between the two remains fuzzy. HTTP, the foundational protocol of the web, once carried data in plaintext, vulnerable to interception and manipulation. HTTPS, its encrypted successor, now underpins nearly every major platform, from banking to social media. The gap between them isn’t just technical—it’s existential for digital safety.
The transition from HTTP to HTTPS didn’t happen overnight. It was a slow burn, fueled by high-profile breaches, regulatory pressure, and the relentless push by tech giants to make the internet safer. Today, the debate isn’t whether to adopt HTTPS, but how quickly to enforce it across legacy systems. The stakes are clear: a single unencrypted connection can expose user data, damage brand credibility, and even trigger legal repercussions under privacy laws like GDPR. Yet despite its ubiquity, many still treat HTTPS as a checkbox—ticked, but not fully understood. The reality is far more nuanced: HTTPS isn’t just about locking data; it’s about verifying identities, preventing tampering, and building an infrastructure where users can trust the very fabric of the web.
For developers, marketers, and business leaders, the choice between HTTP and HTTPS isn’t just a technical decision—it’s a strategic one. A website’s protocol can influence conversion rates, SEO rankings, and even user retention. Google’s algorithm, for instance, now penalizes non-HTTPS sites in search results, while browsers like Chrome and Firefox actively block mixed-content warnings. The message is unambiguous: the web’s future is encrypted. But to navigate this landscape effectively, you need more than surface-level knowledge. You need to understand the why behind HTTPS, the mechanics of encryption, and the long-term implications of sticking with HTTP in an increasingly hostile digital ecosystem.
###
The Complete Overview of HTTP vs HTTPS
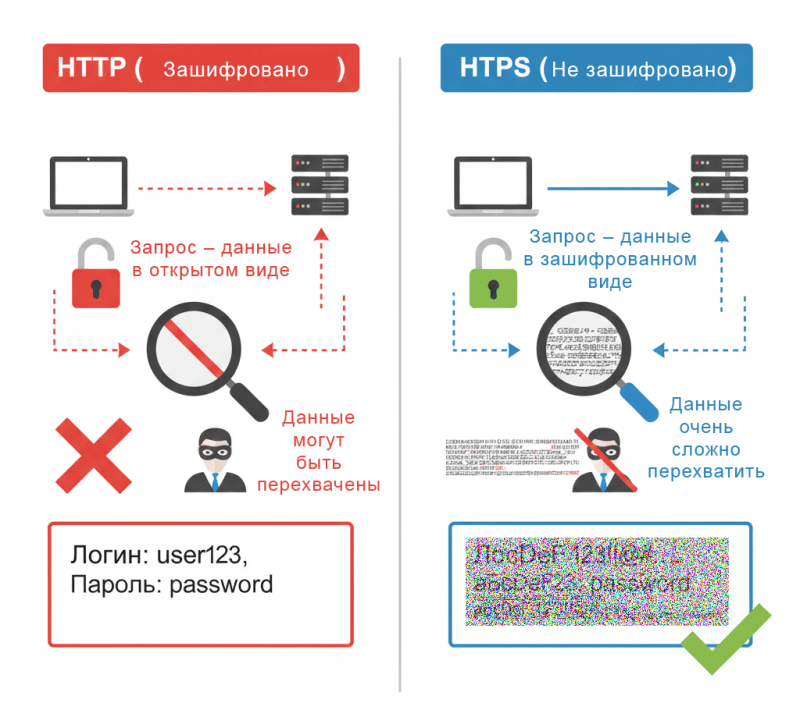
The difference between HTTP and HTTPS boils down to one critical element: encryption. HTTP (Hypertext Transfer Protocol) transmits data between a user’s browser and a website’s server in plaintext, making it susceptible to eavesdropping, data tampering, and man-in-the-middle attacks. HTTPS (HTTP Secure), by contrast, encrypts this data using SSL/TLS (Secure Sockets Layer/Transport Layer Security), ensuring confidentiality and integrity. This isn’t just a minor upgrade—it’s the difference between sending a postcard (HTTP) and a sealed, tracked package (HTTPS). The implications ripple across security, performance, and even legal compliance, particularly in industries handling sensitive data like healthcare, finance, or e-commerce.Beyond encryption, HTTPS introduces another layer of trust through digital certificates. These certificates, issued by trusted Certificate Authorities (CAs), verify that a website is who it claims to be, preventing spoofing attacks where malicious actors impersonate legitimate sites. Without HTTPS, users have no way to confirm a site’s authenticity, leaving them vulnerable to phishing and fraud. The protocol also enforces data integrity, ensuring that the information received hasn’t been altered in transit—a feature critical for transactions, API calls, and any interaction where accuracy matters. The shift from HTTP to HTTPS wasn’t just about security; it was about rebuilding trust in a digital landscape where deception is rampant.
###
Historical Background and Evolution
HTTP emerged in 1991 as the backbone of the World Wide Web, designed by Tim Berners-Lee to enable seamless communication between servers and clients. Initially, its simplicity was its greatest strength: no encryption, no complex handshakes, just raw data transfer. But as the web grew, so did its vulnerabilities. By the mid-1990s, e-commerce was booming, and the need for secure transactions became undeniable. Enter SSL, developed by Netscape in 1995, which added encryption to HTTP. SSL 1.0 was quickly succeeded by SSL 2.0 and 3.0, each addressing new security flaws. However, SSL’s complexity and frequent vulnerabilities led to its eventual replacement by TLS (Transport Layer Security) in 1999, which became the standard for encrypted communications.Table of Contents
- The Complete Overview of HTTP vs HTTPS
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Does HTTPS slow down my website?
- Q: Can I mix HTTP and HTTPS on the same site?
- Q: Are free SSL certificates (e.g., Let’s Encrypt) as secure as paid ones?
- Q: What happens if I don’t switch to HTTPS?
- Q: How do I enforce HTTPS site-wide?
- Q: Does HTTPS protect against all cyber threats?
The adoption of HTTPS was slow in its early years, hindered by performance overhead, cost, and technical complexity. Many websites, especially smaller ones, viewed SSL certificates as an unnecessary expense. But the tide turned in 2014 when Google announced HTTPS would become a ranking signal in its search algorithm—a move that accelerated adoption. By 2017, Google Chrome began labeling all HTTP sites as "Not Secure," and by 2020, over 90% of web traffic was encrypted. Regulatory pressures, such as the EU’s GDPR, further cemented HTTPS as a necessity. Today, the protocol isn’t just a best practice; it’s a baseline expectation for any credible online presence.
###
Core Mechanisms: How It Works
At its core, HTTPS operates by establishing a secure, encrypted connection between a client (e.g., a browser) and a server. This process begins with the TLS handshake, where the server presents its digital certificate to the client. The certificate contains the server’s public key, which the client uses to encrypt a symmetric session key. This key, shared securely, is then used to encrypt all subsequent data exchanged between the two parties. The result is a session where even if data is intercepted, it remains unreadable without the decryption key—a principle known as forward secrecy when ephemeral keys are used.The encryption in HTTPS relies on asymmetric cryptography (public-key infrastructure) for the initial handshake and symmetric cryptography (like AES) for bulk data transfer. Asymmetric encryption is computationally intensive, which is why TLS switches to symmetric encryption once the session key is established. Modern HTTPS also supports OCSP stapling and TLS 1.3, which reduce latency by eliminating unnecessary round trips and improving performance. The protocol’s design ensures not only confidentiality but also authentication (via certificates) and integrity (through hashing algorithms like SHA-256), making it the gold standard for secure communications.
###
Key Benefits and Crucial Impact
The adoption of HTTPS isn’t just a technical upgrade—it’s a cultural shift in how we perceive online security. In an era where data breaches cost businesses an average of $4.45 million per incident (IBM, 2023), the stakes couldn’t be higher. HTTPS mitigates risks by encrypting sensitive data, such as login credentials, payment details, and personal information, rendering it useless to attackers even if intercepted. For businesses, this translates to reduced liability, fewer compliance headaches, and enhanced customer trust. Users, meanwhile, benefit from a safer browsing experience, free from the specter of identity theft or financial fraud.The transition to HTTPS also aligns with broader industry trends, including zero-trust security models and privacy-by-design principles. As governments and organizations tighten data protection laws, HTTPS serves as a foundational layer of compliance. Beyond security, it directly impacts SEO performance, with Google prioritizing HTTPS sites in search rankings. The protocol’s influence extends to user experience, as modern browsers flag HTTP sites with warnings, deterring potential visitors. In essence, HTTPS is no longer optional—it’s a non-negotiable component of digital infrastructure.
> "The web was designed to be an open platform, but openness without security is vulnerability. HTTPS is the lock that keeps the door from swinging both ways." — Moxie Marlinspike, Security Researcher
###
Major Advantages
- Data Encryption: All communications between the client and server are encrypted, protecting against eavesdropping and man-in-the-middle attacks.
- Authentication: Digital certificates verify the server’s identity, preventing spoofing and phishing attacks.
- Data Integrity: Hashing algorithms ensure data isn’t altered during transmission, critical for transactions and API calls.
- SEO Benefits: Google ranks HTTPS sites higher, improving organic visibility and traffic.
- Compliance & Trust: Meets regulatory requirements (e.g., GDPR, PCI DSS) and builds user confidence in handling sensitive data.

Comparative Analysis
| Feature | HTTP | HTTPS |
|---|---|---|
| Encryption | No encryption (plaintext) | TLS/SSL encryption (AES, RSA, etc.) |
| Security Risks | Vulnerable to interception, tampering, and MITM attacks | Protected against eavesdropping, spoofing, and data corruption |
| Performance Impact | Faster (no encryption overhead) | Slightly slower due to handshake and encryption (mitigated by TLS 1.3) |
| Browser Warnings | "Not Secure" labels in Chrome, Firefox | Green padlock icon, "Secure" indicator |
Future Trends and Innovations
The evolution of HTTPS is far from over. One of the most significant advancements is the deprecation of older TLS versions (e.g., TLS 1.0/1.1) in favor of TLS 1.3, which reduces latency and improves security by eliminating obsolete features. Another trend is the rise of HTTP/3, built on QUIC, which further enhances speed and reliability by multiplexing connections over UDP. For enterprises, automated certificate management (via tools like Let’s Encrypt) is reducing the friction of HTTPS adoption, while post-quantum cryptography is being explored to future-proof encryption against quantum computing threats.The next frontier may lie in end-to-end encryption (E2EE), where data is encrypted not just in transit but also at rest, offering even stronger privacy guarantees. However, this raises challenges around lawful access and interoperability. Meanwhile, privacy-focused protocols like DNS over HTTPS (DoH) and HTTP Strict Transport Security (HSTS) are becoming standard, further hardening the web’s security posture. The message is clear: HTTPS is not static—it’s a dynamic ecosystem adapting to new threats and user expectations.
###
Conclusion
The debate over HTTP vs HTTPS is no longer theoretical—it’s a practical imperative. In a digital age where data is the most valuable currency, unencrypted connections are a liability. HTTPS isn’t just about checking a box; it’s about embedding security into the DNA of your online presence. For businesses, the cost of neglecting HTTPS—whether in lost revenue, damaged reputation, or legal exposure—far outweighs the investment in certificates and infrastructure. For users, it’s the difference between browsing with confidence and navigating a minefield of risks.The transition to HTTPS is a collective responsibility. Developers must implement best practices, such as HSTS headers and automatic certificate renewal. Organizations should audit their systems for mixed-content issues and legacy HTTP endpoints. And users? They must demand HTTPS by default, holding websites accountable for their security posture. The web’s future isn’t just encrypted—it’s secure by design. The question isn’t whether to adopt HTTPS, but how swiftly to embrace it before the next wave of threats renders even today’s standards obsolete.
###
Comprehensive FAQs
Q: Does HTTPS slow down my website?
A: Historically, HTTPS introduced minor latency due to the TLS handshake and encryption overhead. However, modern protocols like TLS 1.3 and HTTP/3 have nearly eliminated this gap. In most cases, the performance difference is negligible, and the security benefits far outweigh any speed trade-offs. Tools like KeyCDN’s speed test can help measure real-world impacts.
Q: Can I mix HTTP and HTTPS on the same site?
A: While technically possible, mixed content (loading HTTP resources on an HTTPS page) triggers browser warnings and undermines security. Modern best practices dictate enforcing HTTPS everywhere, including via HSTS headers and 301 redirects from HTTP to HTTPS. Browsers like Chrome block insecure scripts/stylesheets by default, which can break functionality.
Q: Are free SSL certificates (e.g., Let’s Encrypt) as secure as paid ones?
A: Yes. Let’s Encrypt’s certificates use the same 2048-bit RSA or ECDSA keys as paid providers and are issued by a trusted CA. The only difference is cost—free certificates require more manual renewal (typically every 90 days). For most use cases, free certificates are sufficient, though enterprises may opt for extended validation (EV) certificates for additional trust indicators.
Q: What happens if I don’t switch to HTTPS?
A: Beyond browser warnings, non-HTTPS sites face:
- Lower SEO rankings (Google penalizes HTTP sites).
- Compliance risks (GDPR, CCPA fines for unencrypted data).
- Increased vulnerability to attacks (e.g., session hijacking).
- User distrust (70% of visitors abandon sites marked "Not Secure").
Q: How do I enforce HTTPS site-wide?
A: Use these steps:
- Install an SSL certificate (via your host or Let’s Encrypt).
- Update your site’s configuration to redirect HTTP → HTTPS (e.g., `.htaccess` for Apache or server blocks for Nginx).
- Add an HSTS header (`Strict-Transport-Security: max-age=31536000`) to enforce HTTPS permanently.
- Audit for mixed content using browser dev tools or SecurityHeaders.com.
Q: Does HTTPS protect against all cyber threats?
A: No. HTTPS secures data in transit but doesn’t defend against:
- Client-side vulnerabilities (e.g., malware on a user’s device).
- Server-side breaches (e.g., database leaks).
- Social engineering (e.g., phishing emails).
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Seuclienteoculto.